

Microsoft is moving millions of users off SMS and onto passkeys, and most admins now have to decide which kind of passkey each group of users should get. Nishant Kaushik, CTO of the FIDO Alliance, the industry body behind the passkey standards, explains the three flavours of workforce passkey, how to roll out hardware security keys without repeating the RSA token years, and why passkeys are your best route to the post-quantum cryptography deadlines.
Key takeaways
Pick the right passkey for each user
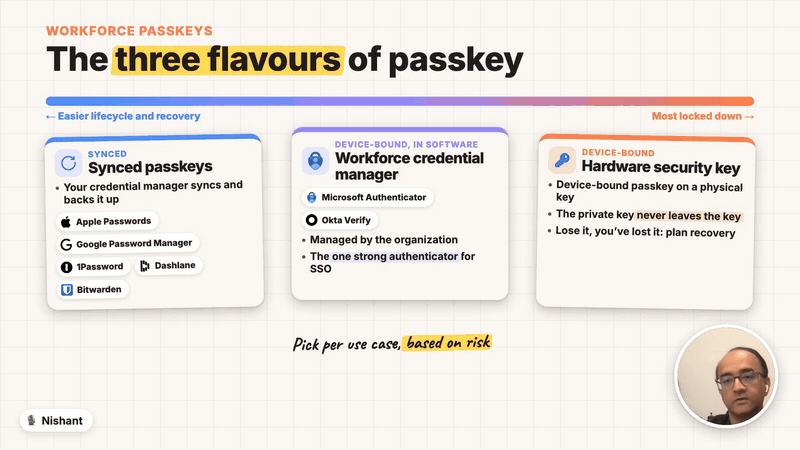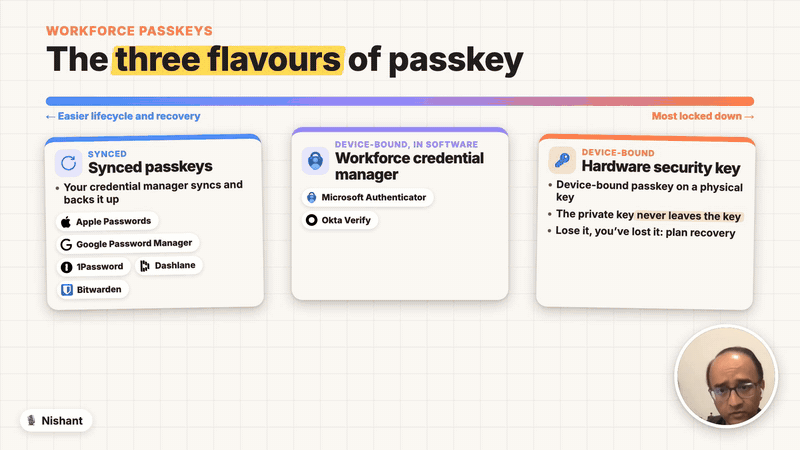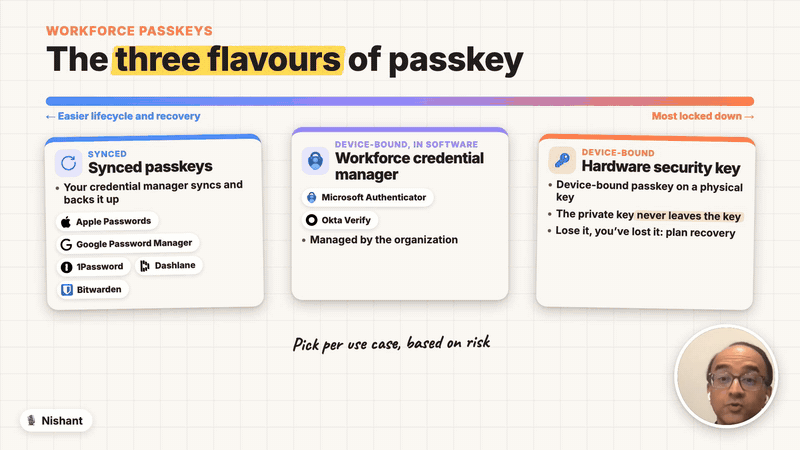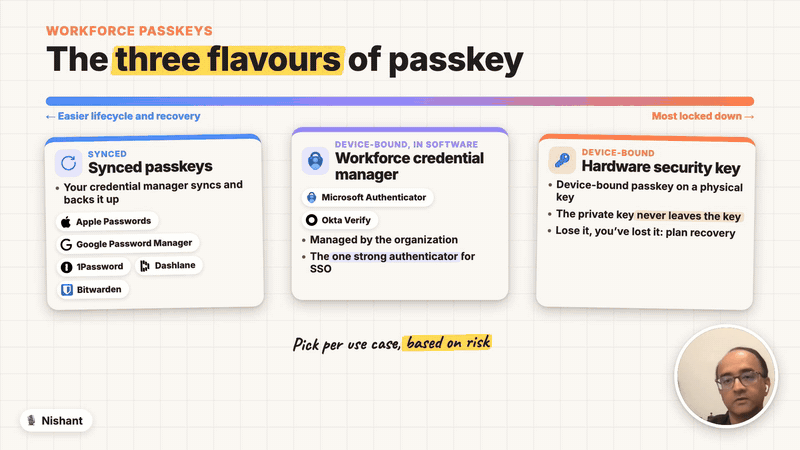
Passkeys are about phishing, not passwords. The FIDO Alliance set out to build phishing-resistant authentication that ordinary users never have to understand: public-key cryptography with the key management hidden in a credential manager or a security key. Judge every method by that test. Stacking phishable factors, such as a password, an SMS code and a push approval, only gives an attacker several things to phish, and that is easy to automate.
Know the three flavours. Synced passkeys live in a credential manager that backs them up and restores them when a phone is lost. Device-bound passkeys on a hardware security key never leave the key: lose it and it’s gone. In the middle sits the option most people miss, a device-bound passkey in a workforce credential manager such as Microsoft Authenticator, managed by the organisation and used as the one strong authenticator for single sign-on.
Match the flavour to the risk, then run it like any IT project. Assess your users, segment them, apply the control that fits each segment’s risk, and plan the whole lifecycle: onboarding, use, monitoring, recovery, revocation and deprovisioning. Synced passkeys didn’t take security away from device-bound ones; they gave you another option for the users who need it.
Check what Microsoft’s rollout has already done in your tenant. Since 1 September 2026, users enabled for SMS and voice have been enabled for passkeys and prompted to register them unless an admin opted out, ahead of Microsoft-provided SMS and voice MFA retiring on 1 February 2027 (1 July 2027 for Global Administrators and external users). Unless passkey profiles or attestation restrict them, those users can register synced passkeys. Before you push back, ask whether the new method is better than the SMS code it replaces. For almost every user, it is.
Roll out hardware keys with intention
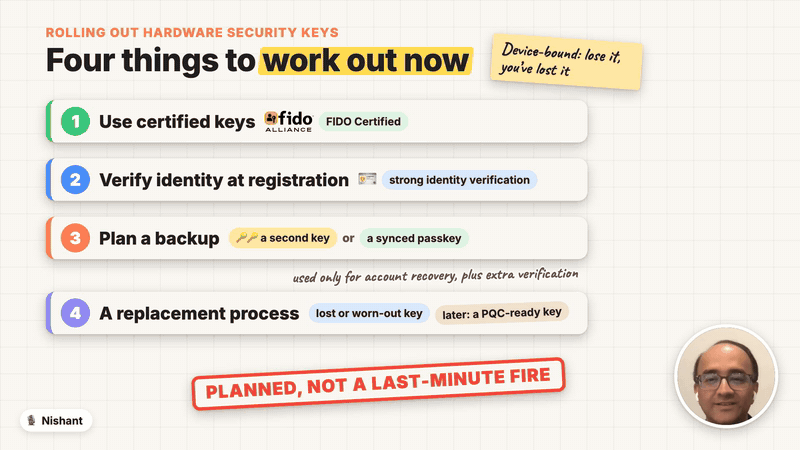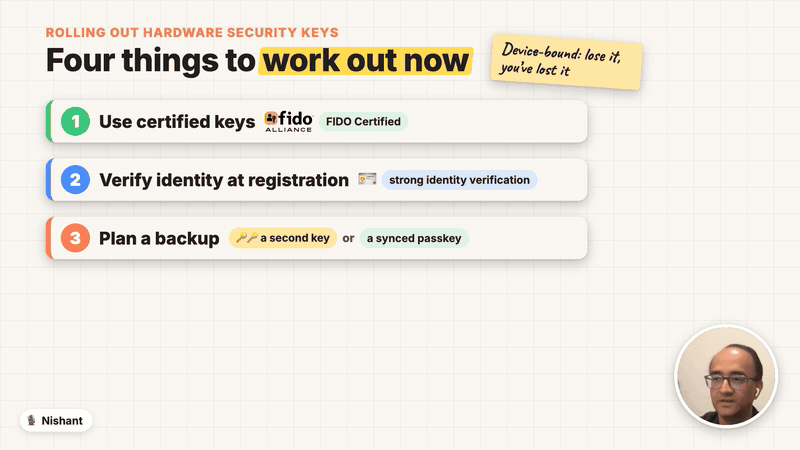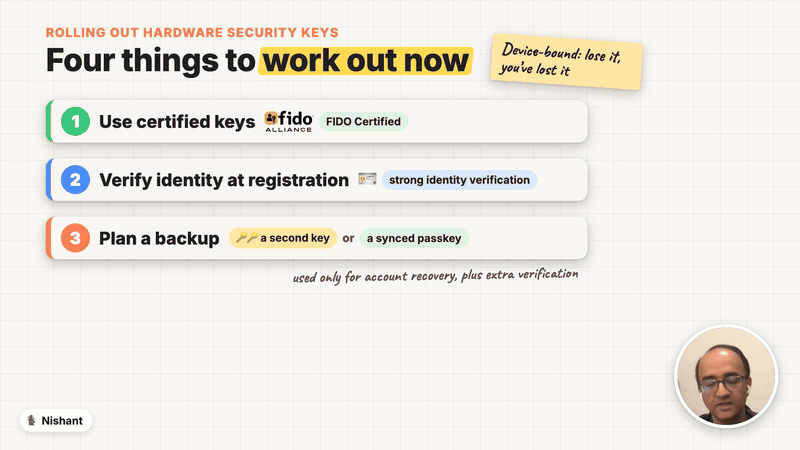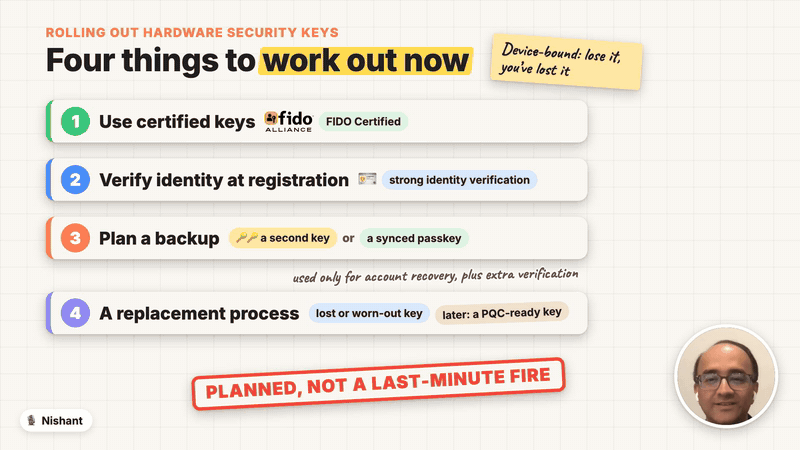
Buy certified keys and bind them to a verified person. Use FIDO Certified security keys that your identity provider accepts. The best authenticator in the world is worth little if you don’t know who you handed it to, so tie registration to strong identity verification of the user.
Plan the backup and the replacement before you need them. A device-bound key that’s lost is lost. Decide whether each user gets a second key or a synced passkey used only for account recovery alongside another check, and write the process for replacing a lost or compromised key. You’ll reuse that process when post-quantum-ready keys arrive.
Get a head start on post-quantum cryptography
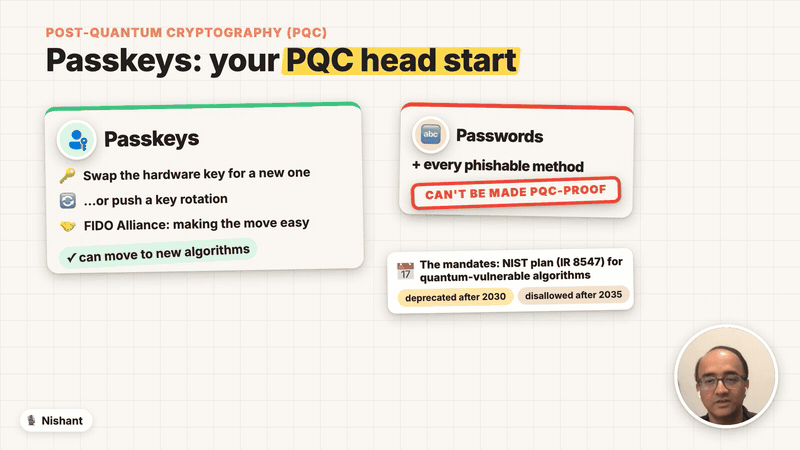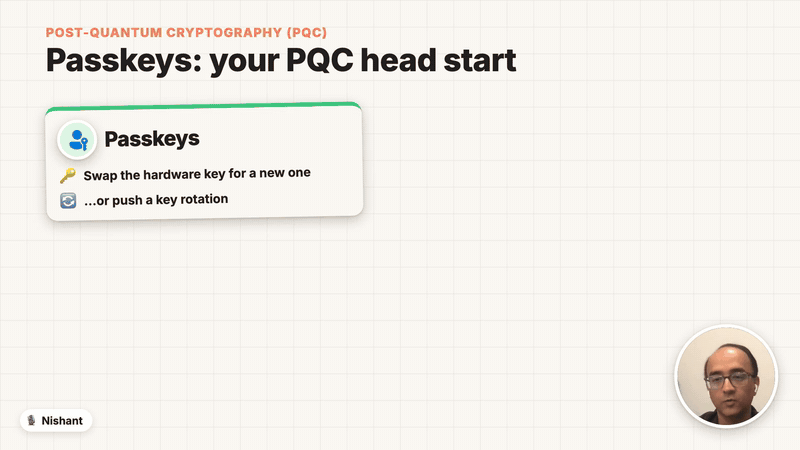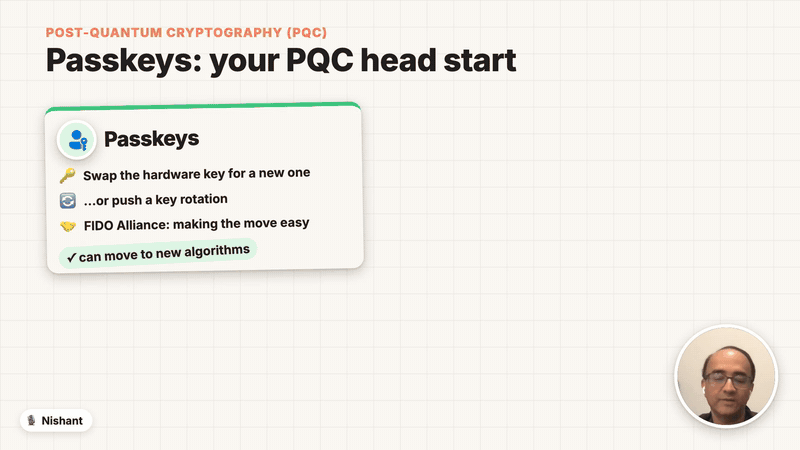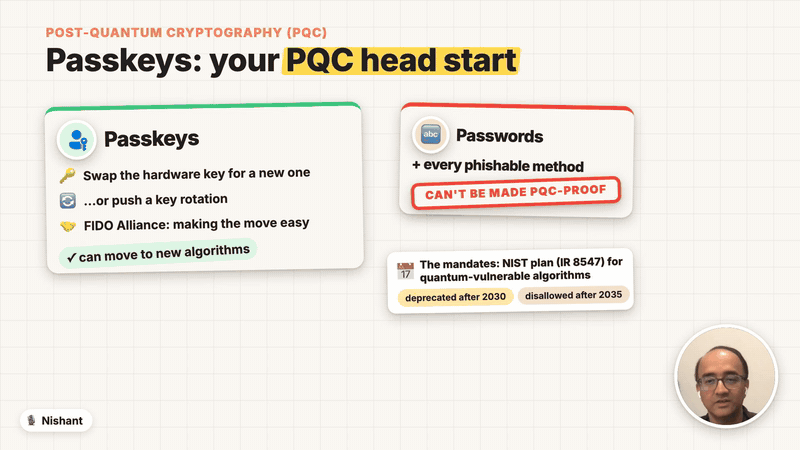
Start the PQC work now. A cryptographically relevant quantum computer could break the classical public-key cryptography behind TLS certificates, PKI and today’s passkeys, and some post-quantum cryptography (PQC) mandates land by the end of 2030. There were no PQC-ready hardware security keys on the market when this was recorded, but passkeys can move to new algorithms through a key rotation or a key swap. You can’t make a password or any other phishable method PQC-proof. The organisations that have already deployed passkeys and rehearsed key replacement will make that switch as a routine change rather than a scramble.
Watch the full conversation for how the FIDO standards came together, the running “year of PKI” joke, why Nishant’s kids pasted their password-manager passwords into a Google Doc, and the HTTP-to-HTTPS moment he thinks passkeys can repeat.
The FIDO Alliance published its Passkey Index 2026 on 15 October 2026, ahead of Authenticate 2026 (19-21 October, Carlsbad, California). Across the consumer services in the index, passkeys were used in 36% of successful sign-ins, up from 26% in 2025, and passkey sign-ins succeeded 93% of the time against 78% for traditional MFA. Read it at fidoalliance.org/passkey-index-2026.
Subscribe with your favorite podcast player or watch on YouTube
About Nishant Kaushik
Nishant Kaushik is the Chief Technology Officer of the FIDO Alliance, the industry association behind the FIDO standards that power passkeys. He has spent more than 25 years in digital identity and security, including CTO roles at Uniken and SCUID, Chief Architect at Identropy and Lead Strategist for Identity Management at Oracle. He writes the Talking Identity blog, serves on the RSA Conference Program Committee and the Identiverse Content Advisory Board, and is based in New York.
Website - nishantkaushik.com
Blog - blog.talkingidentity.com
LinkedIn - https://www.linkedin.com/in/nishantkaushik
Bluesky - https://bsky.app/profile/nishantkaushik.com
Related Links
From the conversation:
FIDO Alliance Passkey Index 2026, published 15 October 2026 (mentioned at 44:15) - https://fidoalliance.org/passkey-index-2026/
Authenticate, the FIDO Alliance conference, held 19-21 October 2026 in Carlsbad, California (mentioned at 44:23) - authenticatecon.com
Passkeys by default and the retirement of Microsoft-provided SMS and voice authentication (mentioned at 02:10) - https://learn.microsoft.com/entra/identity/authentication/concept-sms-voice-retirement
SMS and voice retirement FAQ, including third-party telephony providers - https://learn.microsoft.com/entra/identity/authentication/concept-sms-voice-retirement-faq
What is the FIDO Alliance? (mentioned at 02:52) - https://fidoalliance.org/overview/
FIDO specifications: UAF, U2F, and FIDO2 with WebAuthn and CTAP (mentioned at 08:01) - https://fidoalliance.org/specifications/
W3C Web Authentication (WebAuthn) (mentioned at 08:17) - https://www.w3.org/TR/webauthn/
FIDO Certified Products directory (mentioned at 10:11 and 34:02) - https://fidoalliance.org/certification/fido-certified-products/
ASD Essential Eight maturity model changes: phishing-resistant MFA at Maturity Level Two (mentioned at 12:31) - https://www.cyber.gov.au/business-government/asds-cyber-security-frameworks/essential-eight/essential-eight-maturity-model-changes
Configure Essential Eight MFA with authentication strengths in Microsoft Entra - https://learn.microsoft.com/compliance/anz/e8-mfa-configure-authentication-strengths
NIST SP 800-63B-4: Authenticator Assurance Levels (mentioned at 13:00) - https://pages.nist.gov/800-63-4/sp800-63b/aal
UK NCSC: Passkeys are more secure than traditional ways to log in (mentioned at 13:25) - https://www.ncsc.gov.uk/blogs/passkeys-are-more-secure-than-traditional-ways-to-log-in
Death and the Digital Estate Community Group, OpenID Foundation (mentioned at 24:55) - https://openid.net/cg/death-and-the-digital-estate/
FIDO Alliance white paper: Addressing FIDO Alliance’s Technologies in a Post Quantum World (mentioned at 32:32) - https://fidoalliance.org/white-paper-addressing-fido-alliances-technologies-in-post-quantum-world/
NIST IR 8547: Transition to Post-Quantum Cryptography Standards (mentioned at 37:58) - https://csrc.nist.gov/pubs/ir/8547/final
Passkeys in Microsoft Entra ID:
Enable passkeys (FIDO2) and passkey profiles (mentioned at 16:02) - https://learn.microsoft.com/entra/identity/authentication/how-to-authentication-passkeys-fido2
Enable synced passkeys in Microsoft Entra ID - https://learn.microsoft.com/entra/identity/authentication/how-to-synced-passkeys
Enable passkeys in Microsoft Authenticator (mentioned at 17:46) - https://learn.microsoft.com/entra/identity/authentication/how-to-enable-authenticator-passkey
Temporarily opt out of the automatic passkey enablement (mentioned at 27:55) - https://learn.microsoft.com/entra/identity/authentication/concept-sms-voice-retirement#temporarily-opt-out-of-the-automatic-passkey-enablement
Conditional Access authentication strengths (background for “stop thinking in factors”, mentioned at 22:03) - https://learn.microsoft.com/entra/identity/authentication/concept-authentication-strengths
Plan a phishing-resistant passwordless authentication deployment (mentioned at 19:08) - https://learn.microsoft.com/entra/identity/authentication/how-to-deploy-phishing-resistant-passwordless-authentication
Persona considerations for a phishing-resistant passwordless deployment - https://learn.microsoft.com/entra/identity/authentication/how-to-plan-persona-phishing-resistant-passwordless-authentication
Microsoft Entra ID attestation for passkey (FIDO2) vendors - https://learn.microsoft.com/entra/identity/authentication/concept-fido2-hardware-vendor
Configure a Temporary Access Pass for onboarding (mentioned at 34:29) - https://learn.microsoft.com/entra/identity/authentication/howto-authentication-temporary-access-pass
Related Entra.Chat Episodes
How General Motors Moved 200,000 People to Passkeys - https://entra.news/p/how-general-motors-moved-200000-people
From SMS MFA to Passkeys: A Practical Microsoft Entra Migration Plan - https://entra.news/p/from-sms-mfa-to-passkeys-a-practical
Pass-the-Passkey: What Michael Grafnetter’s Black Hat Research Means for Entra Admins - https://entra.news/p/pass-the-passkey-what-michael-grafnetters
Chapters
01:05 Intro
01:23 Passkeys with the CTO of the FIDO Alliance
02:35 What is the FIDO Alliance?
05:55 Where passkeys came from
10:23 Standards, regulators and the Essential Eight
13:46 Which passkey should your users get?
19:35 Synced vs device-bound: the mental model
23:12 Kids, AirDrop and real-world passkeys
27:52 Microsoft’s passkey rollout
31:05 Buying hardware security keys
36:48 Post-quantum cryptography: the 2030 deadline
41:07 Top tip: use passkeys
42:06 Not all authenticator apps are equal
43:49 The Passkey Index and thanks
Podcast Apps
Entra.Chat - entra.chat
Apple Podcast - https://entra.chat/apple
YouTube - https://entra.chat/youtube
Spotify - https://entra.chat/spotify
Overcast - https://entra.chat/overcast
Pocketcast - https://entra.chat/pocketcast
Others - https://entra.chat/rss
Merill’s socials
YouTube - youtube.com/@merillx
LinkedIn - linkedin.com/in/merill
Twitter - twitter.com/merill
TikTok - tiktok.com/@merillf
Bluesky - bsky.app/profile/merill.net
Mastodon - infosec.exchange/@merill
Threads - threads.net/@merillf
GitHub - github.com/merill


