


👋 Hi, Merill and Joshua here with this week’s roundup of the latest news on Microsoft Entra from around the globe 🌍.
Apologies for the slightly late newsletter this week. I had way too much fun at the HIP Conference in Nashville, managed to pick up a bug on the way home, and I’m only just recovering from all the excitement 😀
Don’t forget to check out this weeks podcast with none other than the ‘Yoda of Microsoft Entra’ Tarek Dawoud, sharing some deep insights into AD and Entra.
Microsoft Security Architect: Active Directory Is 10x Harder to Defend Than Entra

At Black Hat USA 2026, Microsoft’s David Weston put three numbers on a slide that anyone still running domain controllers should sit with. The Microsoft Security Response Center went from 80 patches in February to 1,142 at the July Patch Tuesday. The fastest observed breakout time dropped from 98 minutes to 27 seconds. And mean time-to-exploit flipped f…
Enjoy!
Sponsored by:

EasyEntra: Empower First-Level Support to Work Efficiently
Managing standard first-level user support in a hybrid environment is overly complex. To handle even basic tasks, your team needs expertise across multiple platforms like ADUC, Exchange on-premises Admin Center, M365 Admin Center, Entra Admin Center, EXO Admin Center, EXO PowerShell, and Entra Connect PowerShell.
EasyEntra eliminates this complexity and allows first-level support to work without headaches:
✅ Intuitive - The interface mimics the familiar AD Users & Computers layout.
✅ Consolidated - Manage all user settings from a single-pane-of-glass.
✅ Responsive - Preloads all properties for lightning-fast navigation of settings.
✅ Reduces junior IT training - Onboard junior IT staff in minutes.
✅ Protects senior IT staff - Prevent first-level support tickets from escalating.
⚡️ Microsoft
📖 Read
Passkey-themed social engineering leads to identity and cloud compromise • Microsoft Security Research
Protecting organizations from AI-assisted executive impersonation and invoice fraud • Microsoft Security Research
🗣️ Message Center
Sponsored by:

Retiring MIM? Modernise identity sync with DirSync
Microsoft Identity Manager (MIM) is approaching end of life in 2029, leaving many organisations searching for a modern, supported approach to directory synchronisation even in complex and disconnected environments. If you’re still relying on MIM, now is the time to start planning your transition.
PowerSyncPro DirSync is a low-maintenance alternative designed for modern identity environments. Synchronise users, groups, contacts, passwords, and SID history across Active Directory, Microsoft Entra ID and Google Workspace, supporting coexistence, mergers, acquisitions, and large-scale transformation projects.
With advanced matching, attribute rewriting, What-If reporting and near real-time synchronisation, DirSync helps reduce operational overhead while giving IT teams greater control and visibility.
Learn more about PowerSyncPro DirSync or read our blog.
See how PowerSyncPro DirSync can help you move beyond MIM.
From the community…

🚀 Most popular posts from last week
🥇 Passkey as first MFA method: What could go wrong? • Per-Torben Sorensen
🥈 How to Block Personal Windows Devices in Microsoft Intune • Mark Oldham
🥉 The magic of Agent Identities in Microsoft Entra • Gabe Corsini
☀️ Learn
👩✈️ AI & Copilot
AI Agents as Non-Human Identities: Why Autonomy Changes the Governance Problem • Sameer Bhanushali
Blueprint Inheritance Abuse in Entra Agent ID • Elli Shlomo
🧰 Workload ID
Entra ID Continuous Access Evaluation and Microsoft 365 • Tony Redmond
Run a PowerShell Workload on a Local Kubernetes Cluster That Talks to Microsoft Graph • Ben Reader
👮♂️ ID Governance
The Lazy Way to Bulk Access Packages • Sandra Saluti
New feature in PIM - fire custom extensions on role activation • Stian A. Strysse
📦 Apps
Authentication
Switching password managers is easy and safe on Android • Jean-Pierre Pralle
Microsoft Entra expands passkey registration campaigns • Daniel Bradley
Attackers Use Passkey Phishing to Hijack Microsoft Cloud Accounts and Exfiltrate Data • The Hacker News
📺 How to Map Out the Entra Passkey Registration Campaign [Demo] • Ru Campbell
👥 User & Group Management
🤖 DevOps & PowerShell
Microsoft closes a data access gap for Graph API permission • Daniel Bradley
Why Entra Administrators Cannot Disable Their Own Accounts • Tony Redmond
🚦 Conditional Access
Microsoft Entra Conditional Access GPS Location: Why Authenticator Asks to Enable Location • Sreejith Reghunathan Pillai
🥷 Security
🛠️ Audit Entra ID for privilege escalation paths through application permissions, role assignments, and app ownership • Nicolas Blank
Microsoft Security Architect: Active Directory Is 10x Harder to Defend Than Entra • Merill Fernando
Are Your Microsoft Entra Extensions Actually Being Used? • Sebastian Flaeng Markdanner
📒 Tenant Configuration
📺 Episode 436: Finding the Entra Tenants You Didn’t Know You Had • Microsoft Cloud IT Pro Podcast
🔥 Maester
You ran Maester 200 times. Now what? • Mateusz Jendza
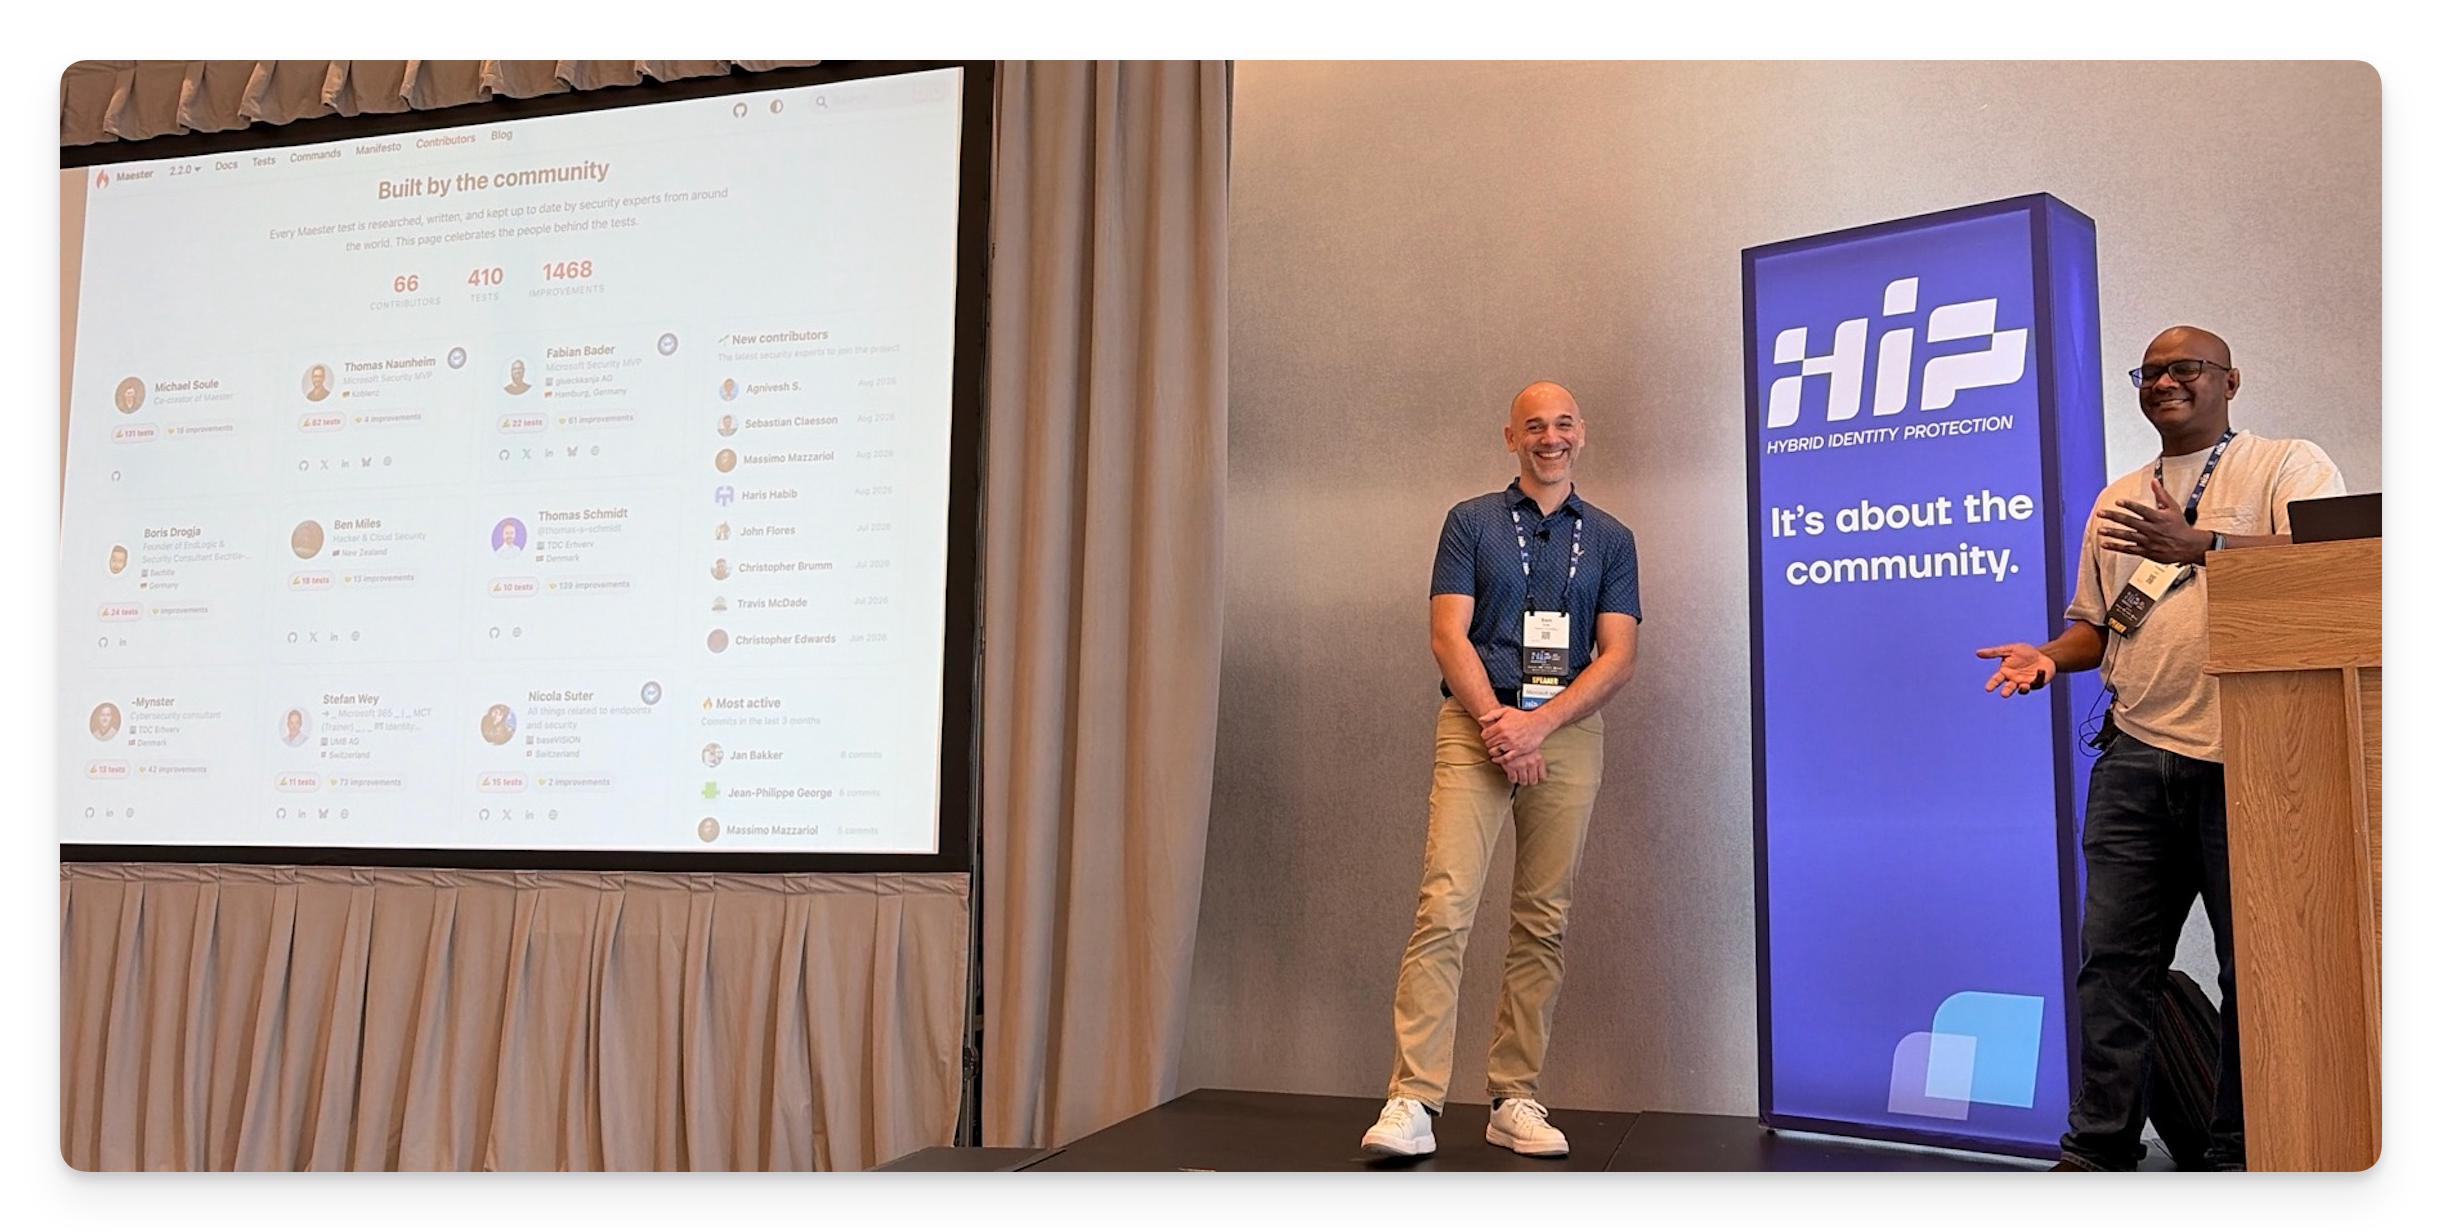
Sam Erde and I had the opportunity to present on Maester with a deep dive into creating custom tests with Maester. We’ll include the link to the recording once it is published.
👨🏽💻 Merill’s corner

Want to get featured on Entra.News? → Submit your content 😎
Want us to say nice things about your company? Sponsor entra.news 🤩
Love the newsletter? Tell us 💚❤️💜
🪃 Acknowledgement of Country
Entra.News is created on Wurundjeri land and acknowledges the traditional owners of country throughout Australia, recognising their continuing connection to land, water and community. We pay our respect to them and their cultures and to elders both past and present.